NEWS
Private Hugging Face Datasets Keep MicrosoftSystem64 Theft Alive
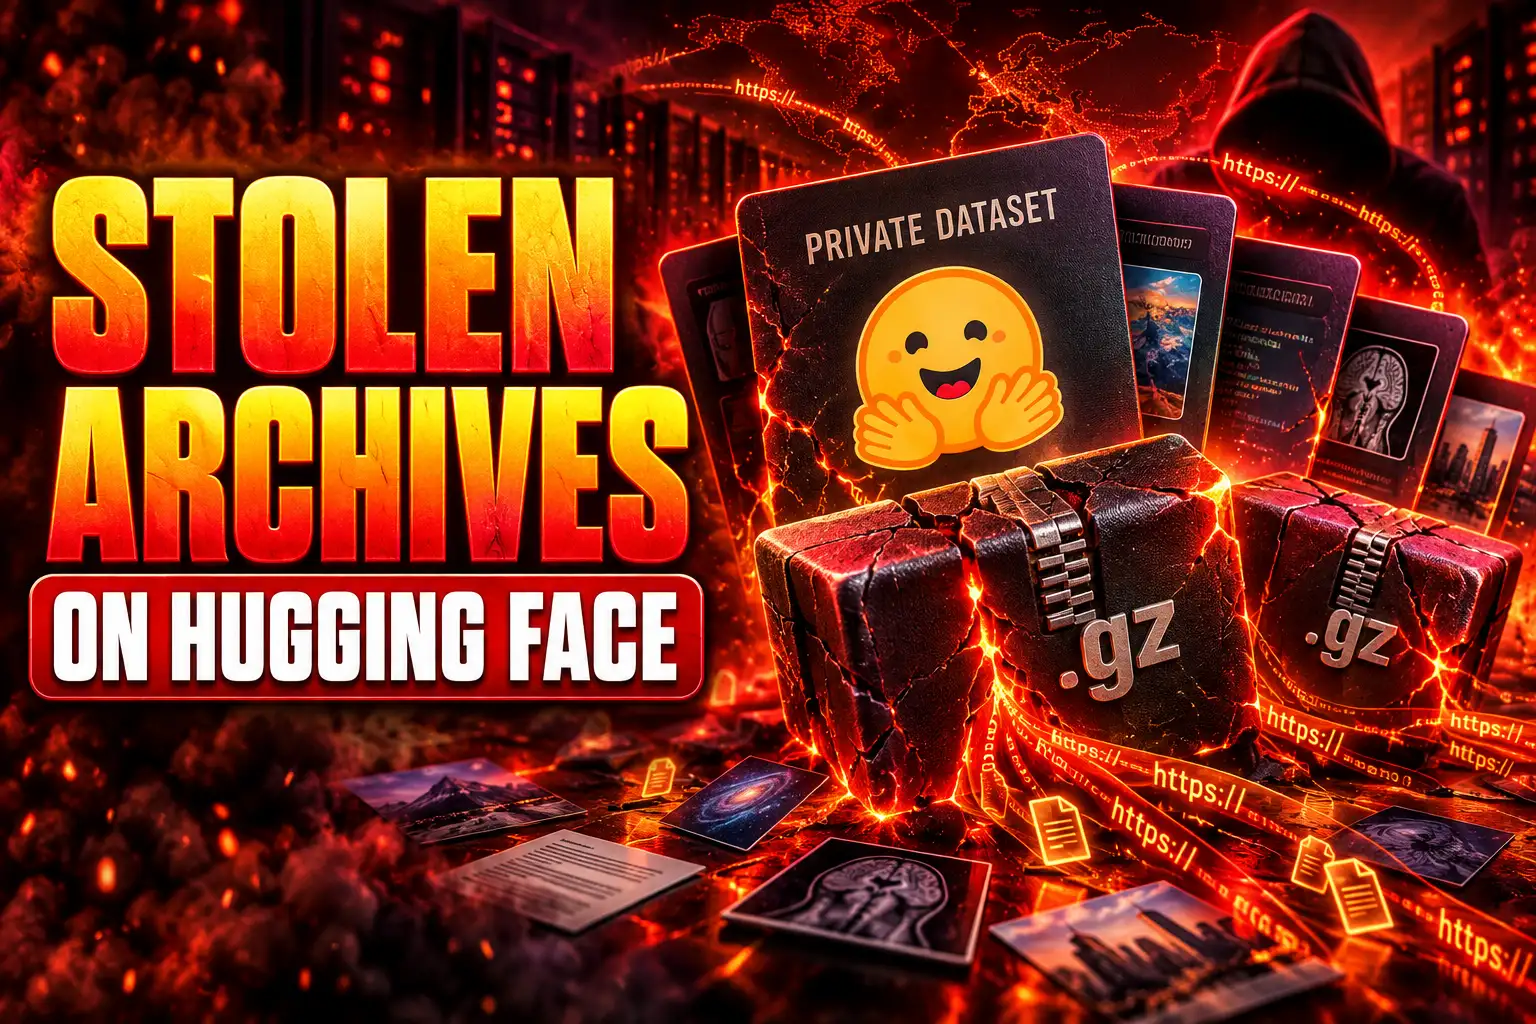
MicrosoftSystem64 sent stolen screenshots and a 500 MB credential dump to private Hugging Face datasets that public malware scans never see.

MicrosoftSystem64 sent stolen screenshots and password stores to private Hugging Face datasets, hiding the theft in ordinary AI traffic. The implant arrived through a fake npm logger, then kept watch on Windows, macOS, and Linux after two public write-ups in April 2026.
SafeDep’s May 28 probe found the Hugging Face token still worked, the Hetzner command server still answered, and two real machines were being watched minute by minute. Blocking that German IP would not have pulled the files back. They were already sitting on huggingface.co.
Stolen Archives Landed on Hugging Face
The implant talks to a WebSocket panel at 195.201.194.107 on port 8010, a Hetzner box in AS24940. Heartbeats go out every 15 seconds with an agentId built from the OS, username, and machine id. Bulk loot does not stay on that host.
Shavit Satou of JFrog Security Research, writing on April 23, 2026, mapped the upload_folder_hf task. The operator sends a token, a username, a path, and an upload id. The implant then archive the folder and upload it as gzip into a private dataset named from the agentId and the path, using the bundled @huggingface/hub client. A small POST to /api/validate/hf-upload-complete tells the panel which dataset to open.
Failed jobs are stored in ~/.pcl-state/uploads.json and retried after a reconnect. If antivirus deletes the local archive, the agent packs the original folder again. Network tools that only watch the Hetzner IP miss the heavy copy, because that copy is signed-in HTTPS to a site many developer laptops already use.
The same Hub path also hosts the implant. From js-logger-pack 1.1.22 onward, a postinstall script pulled MicrosoftSystem64-win.exe, MicrosoftSystem64-linux, MicrosoftSystem64-darwin-x64, or MicrosoftSystem64-darwin-arm64 from a public model repo. The running binary checks that repo every 24 hours, with a first check at 60 seconds, and replaces itself if version.txt moved. JFrog found no signature check on the swap. One commit message on the repo even read “v1.0.1: rebuild with upload_folder_hf support.”
Public Malware Scans Missed the Private Datasets
Hugging Face already looks for hostile files on the Hub. Its docs say it runs every file through a malware scanner (ClamAV) on each commit, and it badges infected public files. On October 22, 2025, the company said VirusTotal would continuously scan public model and dataset repositories, then 2.2 million of them. Hash lookups run when a visitor opens a repo page. Raw bytes are not sent.
That design is aimed at a poisoned model someone might download. It is not aimed at a private dataset that only the token holder can list. A gzip of Chrome Login Data, an SSH key, or a base64 PNG is not a virus. ClamAV has nothing to flag. VirusTotal never sees the hash. The Content Policy, effective April 10, 2025, already bans malware and “excessive or irrelevant data,” but a private repo is visible only to its owner, so Hub users cannot open a public report on the loot pile.
Hugging Face did act on the public binary host. It did not close the private side in time for SafeDep’s May 28 check.
HUGGING FACE ACCOUNTS ON MAY 28
| Account | Created | Role | Status on May 28, 2026 |
|---|---|---|---|
| Lordplay | November 24, 2025 | Public system-releases binaries | Account up; file downloads returned 401 |
| jpeek998 (display name Jlob) | May 15, 2026 | Private dataset uploads | Fully active; embedded token still worked |
Lordplay was not a one-day sock. JFrog’s Hub metadata showed six older sports and computer-vision models from February 2026 as cover. The malicious system-releases repo appeared on April 19, 2026. Hugging Face later cut file access but left the repo listing and the account. SafeDep said jpeek998 was created 13 days after that cut, with no public repos, as the new upload target. The token baked into the 1.0.8 binary authenticated as jpeek998 with read and write rights on private datasets. SafeDep said it reported the token for revocation. Later public IOCs still named the jpeek998 path.
The npm Logger Grew Through 29 Versions
js-logger-pack posed as a zero-dependency console logger with timestamps and emoji level icons. The published Logger class did nothing on the network. The harm lived in postinstall, which ran node print.js (later print.cjs) and detached so npm install looked finished.
SafeDep counted 29 versions from 0.0.1 on April 1, 2026, through 1.1.26 on April 20. Downloads were 3,726 from April 1 through April 13, with spikes on days a new build shipped, and zero before the campaign. The npm maintainer was jpeek868. The author field said toskypi. All early publishes shared one gitHead. JFrog later pulled 1.1.27, still a Hugging Face dropper.
THE APRIL BUILD ON NPM
- April 1, 2026: Harmless probe versions land; the README still names an older slug, pretty-changelog-logger.
- April 2, 2026: Version 1.1.5 is the first armed build. Unobfuscated logger.ts leaks an SSH public key comment, bink@DESKTOP-N8JGD6T, and the first C2 host, api-sub.jrodacooker.dev.
- April 15, 2026: SafeDep publishes. Hours later 1.1.20 is a re-obfuscation with a new hash. At 20:11 UTC, 1.1.22 swaps the in-package stealer for a Hugging Face binary dropper and bundles @huggingface/hub.
- April 20, 2026: Versions 1.1.25 and 1.1.26 shrink the dropper and rename the hook to print.cjs. Six builds shipped after the first public flag.
- April 22, 2026: The GitHub Advisory Database lists the family. SafeDep said npm took the package down the same day.
Early Linux builds also wrote the attacker’s RSA key into ~/.ssh/authorized_keys. From 1.1.7 the C2 moved to the raw Hetzner IP. OSV tracks the family as MAL-2026-2827. JFrog Xray ids include XRAY-965126 for the npm package and XRAY-968550 for Lordplay/system-releases.
Two Desktops Were Watched in Near Real Time
SafeDep used the live token on May 28, 2026, and listed three private datasets under jpeek998. Two machines were in the sample: an Ubuntu box and a Windows box. Screenshots were JSON wrappers around base64 PNGs, taken every 60 seconds.
DATASETS OPENED ON MAY 28
| Dataset role | Host | Files | Window (UTC) | Size |
|---|---|---|---|---|
| Screenshot stream | Ubuntu | 323 | May 27, 23:51 to May 28, 05:14 | ~167 MB |
| Screenshot stream | Windows | 94 | May 28, 03:41 to May 28, 05:14 | ~16 MB |
| scan_files archive | Windows | 1 gzip | May 28, 03:43 | 500 MB |
Researchers decoded 417 screenshots from both datasets. The Ubuntu desktop showed a crypto terminal (MT5 on Binance EUR/BTC), Python scripts, and Polymarket bot alerts. The Windows desktop showed ChatGPT, a JoinQuant trading screen, and VS Code with exchange tabs. Both targets match the implant’s wallet and browser harvest, not a random home PC.
String extraction on the Windows archive found 1,097 credential files packed in a custom format, not a normal zip. From the C: profile: SSH keys (id_rsa, id_rsa.pub, known_hosts), Chrome and Edge Login Data, Cookies, History, Local State (DPAPI material), Claude Desktop app data, and other Electron stores. A second profile or mapped D: drive added WeChat session data, an anti-detect browser’s shop logins,.rdp files, Todoist, and Telegram. The agent kills browser processes first so those databases unlock.
Dataset names follow a fixed pattern: platform, username, machine-id hash, then an optional suffix (_scan_files, _scan_wallets, _ssh_keys). Create calls go to huggingface.co/api/repos/create. Commits use Git LFS and NDJSON operations. Screenshot jobs can also stream to the C2; Hugging Face is the store that does not need the attacker to pay for object storage.
Why the Process Is Named MicrosoftSystem64
The binary sets process.title to MicrosoftSystem64 and installs under folders of that name, so Task Manager and ps look like a Microsoft background service. The Linux sample SafeDep tore down is 85,134,080 bytes (81 MB), a stripped ELF that is actually a Node.js v20.18.2 Single Executable Application. The same JavaScript blob sits inside the Windows PE and both macOS Mach-O files. JFrog hashed that blob at 1c83019b52be6da9583d28fe934441a74eacef0cd7dbb9d71017122de6fe7cfc. A user does not need Node.js already installed.
Config values are XOR’d with a short key, then left next to plaintext comments in dist/config.js, including the WebSocket URL, the jpeek998 user, and the Hugging Face token. SafeDep listed 24 remote tasks. They cover wallet scans, file pattern scans, Telegram tdata, SSH key theft, a full shell (powershell.exe on Windows, /bin/sh elsewhere, 60 second default timeout), directory and drive listing, a keylogger, clipboard read and write, screenshot streams, and the Hugging Face upload pair.
The keylogger is native on each OS: SetWindowsHookEx plus in-memory C# on Windows, a throwaway Swift helper compiled with swiftc on macOS, xinput then evdev on Linux. Clipboard polling is every 1 second. JFrog also documented clear_sessions, which kills browsers and wipes session stores so the user logs in again while the logger is already running. Those new passwords can sit in a private dataset within minutes.
WHERE THE IMPLANT HIDES AFTER REBOOT
- Windows: Scheduled task \MicrosoftSystem64, Run key HKCU\Software\Microsoft\Windows\CurrentVersion\Run\MicrosoftSystem64, files under %LOCALAPPDATA%\MicrosoftSystem64, plus a.vbs launcher in some builds.
- macOS: LaunchAgent ~/Library/LaunchAgents/com.launchkeeper.MicrosoftSystem64.plist and ~/Library/Application Support/MicrosoftSystem64.
- Linux: ~/.config/systemd/user/MicrosoftSystem64.service, ~/.config/autostart/MicrosoftSystem64.desktop, and ~/.local/share/MicrosoftSystem64.
A.registered file with an ISO timestamp marks first run. Moonlock Lab, on June 25, 2026, described a macOS sample as “a full-featured remote access trojan masquerading as MicrosoftSystem64 and using huggingface legitimate infrastructure for its C2 activities,” and listed the jpeek998 darwin-arm64 URL among its IOCs. The Linux SHA-256 for version 1.0.8 is b2954c945b51dbd6fa88ac72338b7fbf76dec7d9909ceada9d36b21330842c97.
Fresh npm Names Kept the Same Implant Alive
Taking js-logger-pack off the registry on April 22 did not retire the binary. SafeDep tied later May drops to the same Lordplay staging path and the jpeek rotation (jpeek868, jpeek886, jpeek895), with toskypi as the stable author string and tosky.pi1016@gmail.com as a persistent mailbox. kmsec.uk and OX Security independently put that cluster with FAMOUS CHOLLIMA, also tracked as Contagious Interview, the DPRK-linked factory that hits developers with fake job tests and poisoned packages. Other npm names in the same line included polymarket-validator (February 2026) and changelog-logger-utilities (March 15, 2026), which sent loot to Vercel and changelog.rest before the Hugging Face pivot.
PACKAGES TIED TO THE SAME IMPLANT
- April core: js-logger-pack (v1.1.22+ drops MicrosoftSystem64), with JFrog’s later 1.1.27 sample.
- May rotation: terminal-logger-utils (May 20 through 21, RC4/XOR obfuscation), ts-logger-pack as a proxy, pretty-logger-utils, and pinno-loggers under the jpeek895 cluster.
- June names: Microsoft Threat Intelligence on June 3 listed utils-terminal@3.2.1 and logger-active@3.2.1 from npm user hexalpha10, author toskypi, plus HTTP C2 c2-toskypi.onrender.com, still calling huggingface.co/api. Nextron Research on June 11 added hex-type@3.0.2.
Logger-themed throwaway accounts keep clearing the registry because a short README and a postinstall hook still look like a utility. GitHub, which owns npm, published the April 22 advisory. Six weeks later Microsoft Threat Intelligence was still listing new logger slugs on the same WebSocket IP and the same Run key name.
https://x.com/MsftSecIntel/status/2062013269687054695
Any computer that has this package installed or running should be considered fully compromised. All secrets and keys stored on that computer should be rotated immediately from a different computer.
GitHub Advisory Database, GHSA-mj89-jrhm-qxhc
The advisory’s wording covers the whole js-logger-pack family, and the package should be considered fully compromised even after npm uninstall, because startup entries live outside node_modules. Rotate SSH keys, npm and cloud tokens, browser passwords, Telegram sessions, and wallet seeds from a clean machine. Hunt the scheduled task, Run key, LaunchAgent, and systemd unit by the MicrosoftSystem64 name. Treat unexpected huggingface.co/api traffic from a laptop that is not training or fetching models as a live lead, which is the rule Microsoft Threat Intelligence posted with the June 3 IOCs.
Other npm RATs in May, including the forge-jsxy wave, also began pushing stolen files through @huggingface/hub. That copycat step is the leftover from MicrosoftSystem64: private datasets on a trusted AI host are now a known drop box, and a public malware badge on the Hub does not look there.

The Gears 2 PC Port Epic Refused to Ship

Ghost Recon Wildlands Returns at 4K as a Catalog Product

Waterpark Simulator Keeps the $12.99 Price After 1.0

Nurix Puts NuPlay on Microsoft Marketplace to Reach Azure Buyers

Xbox Studio Leaders Detest Game Pass for Devaluing $40 Games

Warzone Leaves Xbox One and PS4 After Season 06

Microsoft AI Was Set Free to Build Its Own Frontier

Microsoft IQ Turns Workplace Data Into a Metered Agent Brain

Xbox Games Showcase 2026 Split the Catalog in Two

Nadella Banned Addiction Talk While Scout Kept Heartbeat
-
 NEWS4 months ago
Warzone Leaves Xbox One and PS4 After Season 06
-
 NEWS4 months ago
Microsoft AI Was Set Free to Build Its Own Frontier
-
 MICROSOFT 3654 months ago
Microsoft IQ Turns Workplace Data Into a Metered Agent Brain
-
 NEWS4 months ago
Xbox Games Showcase 2026 Split the Catalog in Two
-
 MICROSOFT 3654 months ago
Nadella Banned Addiction Talk While Scout Kept Heartbeat
-

 NEWS4 months ago
Modern Warfare 4 Splits Its Audience Before the October Launch
-
 NEWS4 months ago
Infinity Ward Bets Modern Warfare 4 on a Paid DMZ
-
 NEWS4 months ago
Dragonwilds Hits Xbox, but Steam Saves Stay Put