NEWS
Silent Ransom Group Hits Law Firms Through Quick Assist
Silent Ransom Group talks law-firm staff into Teams and Quick Assist sessions, copies OneDrive and iManage files, then sends a three-day extortion note.

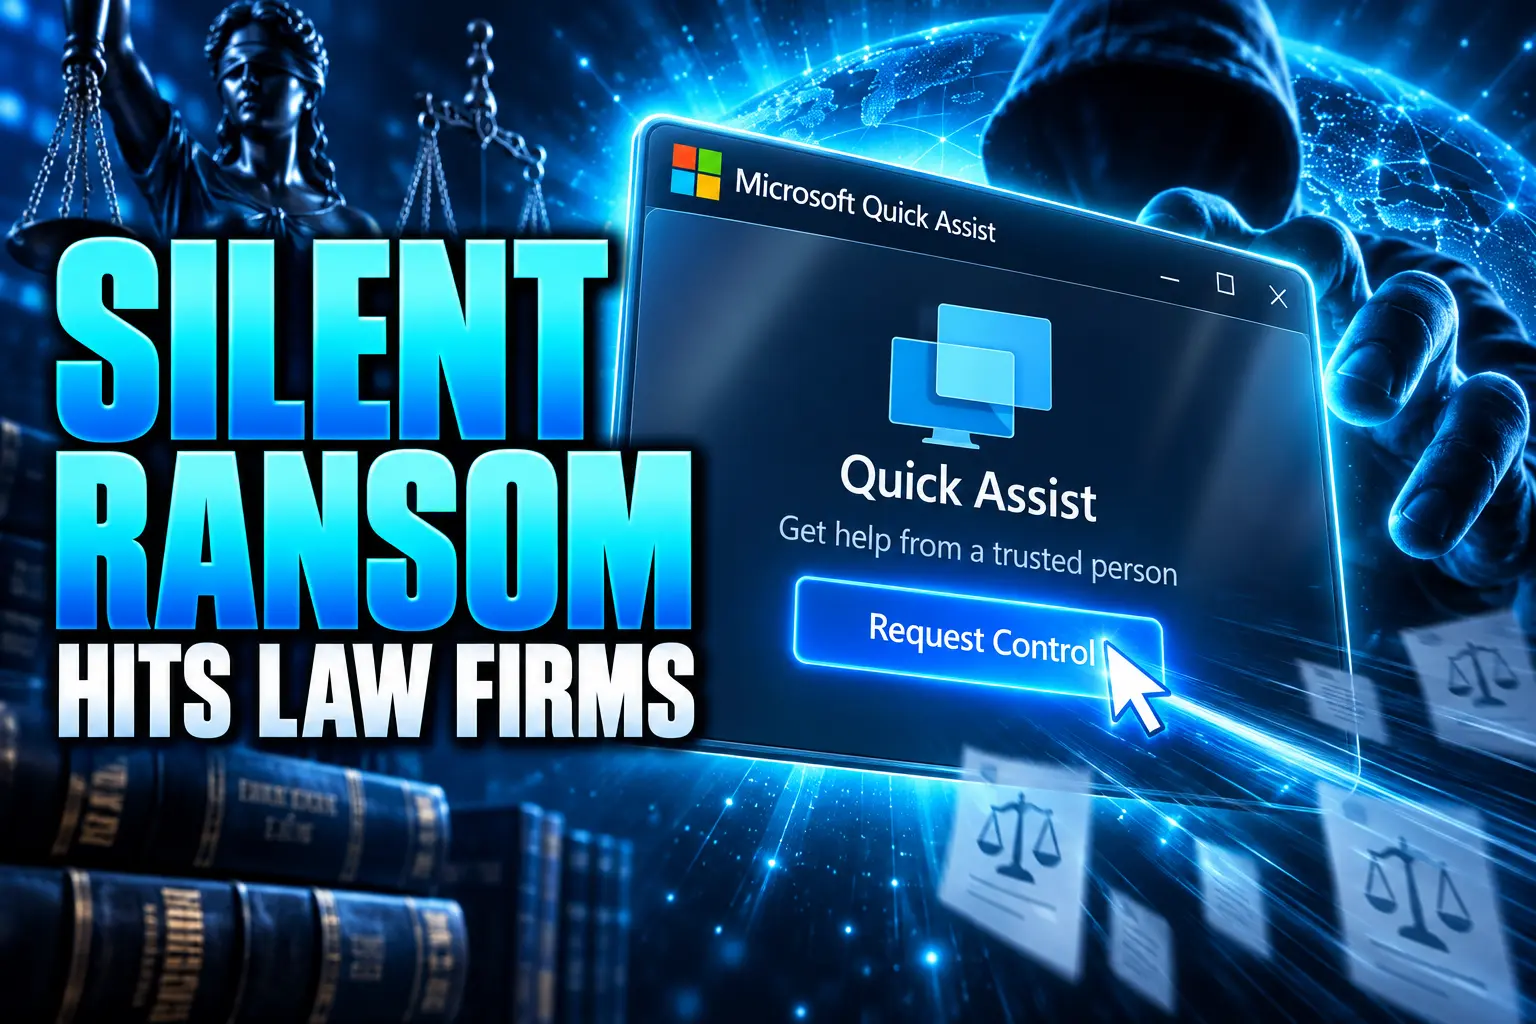
Silent Ransom Group walked staff at U.S. law firms into Microsoft Teams and Quick Assist sessions, then copied client files, Mandiant found in a June 5, 2026 report. Callers posed as internal IT. Mandiant, Google Cloud’s incident response team, tracked the cluster as UNC3753, also known as Luna Moth and Chatty Spider, across dozens of legal, financial, and professional services firms from January through May 2026.
They did not deploy ransomware. They used the remote-support apps Windows shops already trust, then mailed a three-day extortion note, often within 30 minutes of leaving.
Microsoft’s Own Remote Tools Open the Session
UNC3753 gets a live desktop by talking someone into a screen-share, Chad Reams, Tufail Ahmed, Keith Knapp, Ashley Frazer, and Tyler McLellan wrote in Mandiant’s campaign against U.S. law firms. The session runs on Zoom, Microsoft Terminal Services, Microsoft Teams, or Quick Assist. In one Teams case, the same caller held five distinct calls with one target over three days.
Quick Assist ships with Windows 11. The helper sends a short code; the staffer presses Ctrl+Windows+Q, types it, hits Allow, then accepts Request Control. Microsoft Threat Intelligence documented that click path on May 15, 2024, when a different crew, Storm-1811, used the same app as a foothold. The tool has not changed. UNC3753 still asks people to open it.
On September 2, 2026, Microsoft Threat Intelligence mapped a separate Teams helpdesk impersonation attack chain that starts in an external tenant, talks the user past the Accept/Block flags, and lands in Quick Assist. That write-up is not an UNC3753 attribution. It is the same door, still open, on a Microsoft 365 tenant that allows stranger chats.
Once the screen is shared, the crew pushes a commercial remote-monitoring agent so the session outlives the call. Mandiant saw AnyDesk, Bomgar, Zoho Assist, and a SuperOps installer fetched with a quiet cURL command. Links and commands often arrive through privnote.com, a note that deletes itself, so browser history and chat logs keep little.
TOOLS IN THE HELPDESK PATH
| Tool | Where it sits | What the caller uses it for |
|---|---|---|
| Microsoft Teams | Microsoft 365 | Fake helpdesk chat or voice, then screen control |
| Quick Assist | Windows 11, built in | Full desktop control after a short code |
| Microsoft Terminal Services | Windows remote desktop | A second live session if Teams is blocked |
| Windows 365 | Cloud PC client | Pivot from a personal laptop into the firm VDI |
| OneDrive | Microsoft 365 | Search, stage, and copy local legal files |
| AnyDesk, Zoho Assist, Bomgar, SuperOps | Third-party RMM | Access that stays after the call ends |
| WinSCP or Rclone | File transfer | Bulk copy to an outside host |
| privnote.com | Self-destruct notes | Install links that vanish from logs |
Mandiant also saw Zoom opened on a personal BYOD laptop, then a hop into corporate VDI through Windows365.exe or a Citrix client. The helpdesk story travels with the person, not the office PC.
The Harmless Invoice That Starts the Call
Most jobs begin with a dull email from a consumer account. It has no link and no attachment. Mandiant quoted one lure as “hello, here is the invcoie we talked about yesterday.” Google Threat Intelligence Group said the mail’s job is to plant a worry, so the follow-up voice call sounds like IT cleaning up a mess.
Callers scrape names, numbers, and titles from public bios, then phone people at every seniority level. The script is a data migration, a security issue, or an invoice glitch. They stay on the line while the staffer joins the share and installs the agent.
Lookalike IT portals back the story. Mandiant tied registrations to patterns that read as an internal helpdesk. Hunters have seen names that start with the target firm and end in helpdesk. The FBI’s May FLASH on Silent Ransom Group (FLASH-20260526-01, dated May 26, 2026) said actors either call first or mail a prompt that tells the staffer to call “IT.”
Legal services firms represent high-value targets for extortion actors. They maintain concentrated repositories of extremely sensitive client transaction files, merger and acquisition plans, client trade secrets, and corporate regulatory reports.
Chad Reams and Mandiant colleagues, Seeking Counsel, June 5, 2026
Threat groups, Mandiant added, count on legal shops to settle quietly because a leak hits reputation and regulators at once.
What They Copy From OneDrive and iManage
Inside the network, the crew maps local folders, crawls OneDrive, and walks mapped drives. They hunt document platforms next. Mandiant said they use iManage search to pull tax logs (Forms W-2, W-9, and 1099), audit files, client agreements, and Social Security numbers, then dump the pile into Downloads or the Roaming profile.
Copy-out is boring on purpose. Portable WinSCP or a renamed Rclone job. A consumer Drive or OneDrive account opened in the victim’s own browser, sometimes in a folder named like the firm. In one case they told the staffer to mail iManage files to a consumer inbox from the firm mailbox.
ONE INTRUSION, TWO HAULS
- Clock: Mandiant saw searches, staging, and theft start in under an hour, and some jobs finish in a single business day.
- First copy: 1.7 GB left a local OneDrive folder for a Google Drive account the crew controlled.
- Second copy: 14.4 GB more left through WinSCP after a VDI hop, 16.1 GB in that one job.
- Follow-up: Google said it disabled Drive accounts tied to the activity.
The FBI FLASH lists the same cloud path. Stolen files go to Microsoft OneDrive or Google Drive, so the traffic looks like ordinary work. Antivirus rarely flags it, the bureau said, because the apps are legitimate.
Ransom Notes Land Within 30 Minutes
Extortion mail often lands within 30 minutes of the crew leaving. The letters are unbranded. They give the firm three days to answer, then threaten to call and email staff and outside clients. Mandiant said the text leans on lost client trust, regulatory fines, and lawsuits for mishandling files. A later note has threatened to dump archives on the LEAKEDDATA leak site.
One sample told the firm, “Text us today, so We don’t have to start calling your employees tomorrow. You will have 3 days to start communicating.” Screenshots of stolen files ride along as proof.
Resecurity, which tracked the leak host business-data-leaks.com, said the site sits on the open web rather than Tor, and that DNS fast flux rotates it across residential addresses in 18 countries and 22 ISPs. Takedowns bounce off home routers. The same host is the site the FBI named in the FLASH.
A Walk-In With a USB Stick
If the remote session dies, the bureau said the group sends a person. The visitor claims to be IT, says the machine needs an image or a backup after the phishing scare, and plugs in a USB drive or external disk. Mandiant has limited forensic proof on those visits and saw no follow-on extortion in the cases it reviewed, but GTIG still ties the walk-ins to UNC3753 on targeting, timing, and methods. The FBI is the source that treats the physical job as part of Silent Ransom Group’s current playbook.
@FBICyberDiv put the warning in public on May 27, 2026: the group has gone after law firms since 2023, and “since SRG actors use legitimate remote access tools, there are few artifacts of their attacks.”
https://x.com/FBICyberDiv/status/2059696553476939822
That USB step is the part that still sounds theatrical until a receptionist is staring at a stranger who wants a desk and a port. RMM allowlisting is the control that actually cuts the remote half. A logged visitor ID and a dead USB port cut the rest.
WHAT WE KNOW
- The 2026 wave: Mandiant handled dozens of U.S. legal, financial, and professional-services intrusions from January through May 2026.
- The tools: The FBI lists new installs of Zoho Assist, Quick Assist, AnyDesk, RustDesk, Syncro, Splashtop, or Atera as warning signs, plus WinSCP or Rclone to an outside address.
- The pressure: Notes threaten to call employees and clients, then post files on business-data-leaks.com.
WHAT IS UNCONFIRMED
- Every walk-in: Mandiant has not formally attributed each physical visit, citing thin forensics and no extortion in some office cases.
- A public victim tally: Mandiant did not publish a firm-by-firm list for the January through May wave.
The FLASH also asks firms to keep ransom notes, callback numbers, voicemails, wallet addresses, and any photo or camera clip of people who claimed to be IT.
Conti’s Callback Crew Dropped the Encryptor
GTIG dates UNC3753 to at least March 2022 and ties its methods to UNC2686, a cluster that ran Bazarcall-style jobs from early 2021. UNC3753 deployed LockBit Black in 2022, then moved to theft-only extortion on LEAKEDDATA. The old lure was a fake software-renewal PDF with a phone number. Around March 2025 the cluster started posing as the target’s own helpdesk.
The FBI had already flagged the group on May 23, 2025, for IT-themed calls and in-person USB theft at U.S. law firms. The May 26, 2026 FLASH is the follow-up, with Quick Assist named among the remote tools and OneDrive named as a copy-out path. Law-firm targeting, the bureau said, has been consistent since Spring 2023, with insurance, finance, and healthcare hit as well.
THE SHIFT OFF RANSOMWARE
- Early 2021: UNC2686 runs Bazarcall callback phishing that leads to loaders, not a helpdesk voice.
- March 2022: UNC3753 is active; it later uses LockBit Black, then drops encryption.
- Spring 2023: The FBI says U.S. law firms become a steady target.
- March 2025: The cluster starts calling as internal IT helpdesk staff.
- May 23, 2025: The first FLASH warns that failed calls can turn into a person with a USB stick.
- January through May 2026: Mandiant documents the concentrated professional-services wave.
- May 26, 2026: FLASH-20260526-01 restates the IT-impersonation and walk-in pattern.
- June 5, 2026: Mandiant publishes the Teams, Quick Assist, OneDrive, and iManage lifecycle.
- September 2, 2026: Microsoft again maps stranger Teams chats into Quick Assist, a parallel door other crews still use.
The same cluster’s fake IT calls against law firms are the voice layer. The Microsoft stack is what that voice is asking staff to switch on.
An Allowlist for Remote Support Tools
Training still matters, and it is not enough, because the mail has no payload for a filter to catch. Mandiant’s hardening list is mostly about who may run a remote-control binary, who may plug in a stick, and who may walk past reception.
CONTROLS THAT MATCH THIS CREW
- Application control: Block unsigned or unapproved RMM and support tools with Windows Defender Application Control or a third-party equivalent, including AnyDesk, Zoho Assist, and SuperOps.
- Quick Assist: If the helpdesk does not use it, disable Quick Assist in your organization; Microsoft has published that switch since the 2024 abuse wave.
- Teams strangers: Tighten external access so a tenant named Help Desk cannot start a call, and restrict screen-control inside Zoom and Teams where the helpdesk does not need it.
- VDI and BYOD: Allow only firm-owned devices onto VDI or VPN, with an MFA step-up when a personal laptop tries Windows 365 or Citrix.
- USB: Turn off write (and, where you can, read) on removable storage through Group Policy or MDM, including VDI sessions from home PCs.
- iManage and SharePoint: Alert on search spikes and mass downloads, and put MFA on the document store.
- Egress: Watch port 22 from VDI and endpoints for fat WinSCP and Rclone jobs; the FBI says block port 22 if you can.
- Front desk: Copy visitor photo IDs, match technicians to a work order with the real dispatcher, and escort anyone who asks to image a PC.
Microsoft’s September 2, 2026 note is blunt about the user step: the chain holds only if someone overrides the external-contact warnings and grants a live remote session. Silent Ransom Group’s law-firm jobs run on that same grant. The files are already in OneDrive and iManage. The callers are asking staff to hand over the window that shows them.

The Gears 2 PC Port Epic Refused to Ship

Ghost Recon Wildlands Returns at 4K as a Catalog Product

Waterpark Simulator Keeps the $12.99 Price After 1.0

Nurix Puts NuPlay on Microsoft Marketplace to Reach Azure Buyers

Xbox Studio Leaders Detest Game Pass for Devaluing $40 Games

Warzone Leaves Xbox One and PS4 After Season 06

Microsoft AI Was Set Free to Build Its Own Frontier

Microsoft IQ Turns Workplace Data Into a Metered Agent Brain

Xbox Games Showcase 2026 Split the Catalog in Two

Nadella Banned Addiction Talk While Scout Kept Heartbeat
-
 NEWS4 months ago
Warzone Leaves Xbox One and PS4 After Season 06
-
 NEWS3 months ago
Microsoft AI Was Set Free to Build Its Own Frontier
-
 MICROSOFT 3653 months ago
Microsoft IQ Turns Workplace Data Into a Metered Agent Brain
-
 NEWS3 months ago
Xbox Games Showcase 2026 Split the Catalog in Two
-
 MICROSOFT 3653 months ago
Nadella Banned Addiction Talk While Scout Kept Heartbeat
-

 NEWS4 months ago
Modern Warfare 4 Splits Its Audience Before the October Launch
-
 NEWS3 months ago
Infinity Ward Bets Modern Warfare 4 on a Paid DMZ
-
 NEWS3 months ago
Dragonwilds Hits Xbox, but Steam Saves Stay Put